Git security vulnerabilities announced
Git.io github.blog
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.Editor’s note (November 17, 2026): This post has been updated with additional CVE information and updated guidance for GitHub Enterprise Server users. Please see the release information below for the versions that include the fixes.
Today, the Git project is releasing new versions to address six security vulnerabilities. These include arbitrary code execution when cloning a malicious repository, writes to unintended files, and memory corruption when processing merges or binary patches.
More ways to use this
Open on another device
Scan to open this page. Your saved notes and account access are not included.
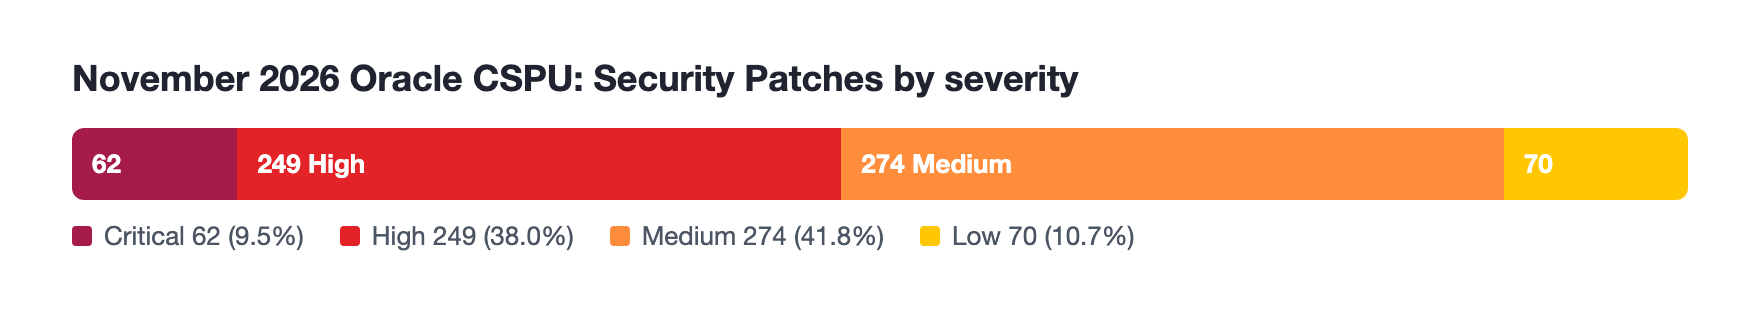 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
 Able2Shell: Frequently asked questions for reported N-able N-central zero-day vulnerabilities