CVE-2026-99317 — In the Linux kernel, the following vulnerability has been resolved: ALSA: hwdep: Serialize DSP load requests The check of the loaded DSP i
ThreatFilter threatfilter.dev
Listen to this summary
(vendor/severity tags below are heuristic) In the Linux kernel, the following vulnerability has been resolved: ALSA: hwdep: Serialize DSP load requests The check of the loaded DSP indices and the call of the driver's dsp_load callback in snd_hwdep_dsp_load() are not serialized. A hwdep file descriptor can be shared among threads, or inherited across fork, so two SNDRV_HWDEP_IOCTL_DSP_LOAD requests for the same index can both observe the index as unloaded and enter the driver's callback concurrently, even though the device itself is opened exclusively. This breaks the assumption behind hw->dsp_loaded that a firmware index is loaded only
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
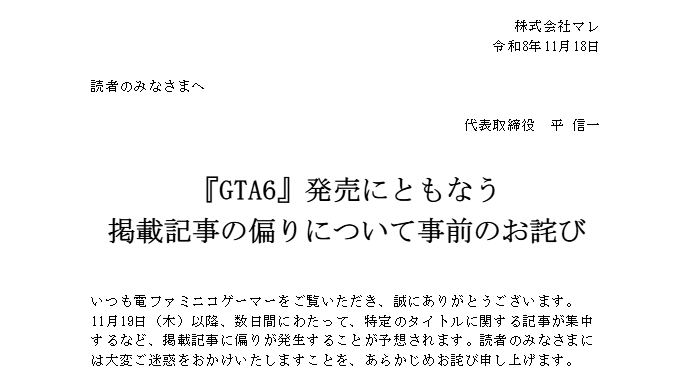 Denfaminicogamer releases an advance apology for the imbalance in article coverage following GTA 6's release
 GiftBot's Gaming Giveaways |OT| Free to a good home! No begging, requests, or taking advantage
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
 Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)