CVE-2026-99319 — In the Linux kernel, the following vulnerability has been resolved: ALSA: usx2y: Refuse a retried DSP load after a failure snd_usx2y_hwdep
ThreatFilter threatfilter.dev
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) In the Linux kernel, the following vulnerability has been resolved: ALSA: usx2y: Refuse a retried DSP load after a failure snd_usx2y_hwdep_dsp_load() sets up the asynchronous sequence URBs and the interrupt URB when the FPGA firmware image with index 1 is loaded, and then creates the ALSA devices. If usx2y_in04_init() or usx2y_create_alsa_devices() fails, the URBs that were already set up are left in place. The core keeps the index unloaded when the callback fails, so user space may issue the same request again. The second attempt then enters usx2y_async_seq04_init() or usx2y_in04_init() with
More ways to use this
Open on another device
Scan to open this page. Your saved notes and account access are not included.
 Cricket Australia refuses to reopen sandpaper investigation
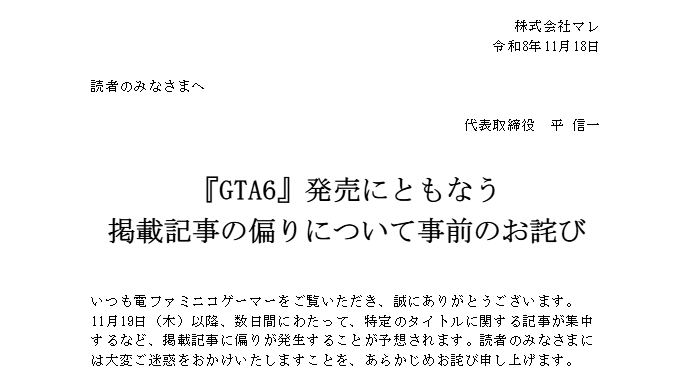 Denfaminicogamer releases an advance apology for the imbalance in article coverage following GTA 6's release
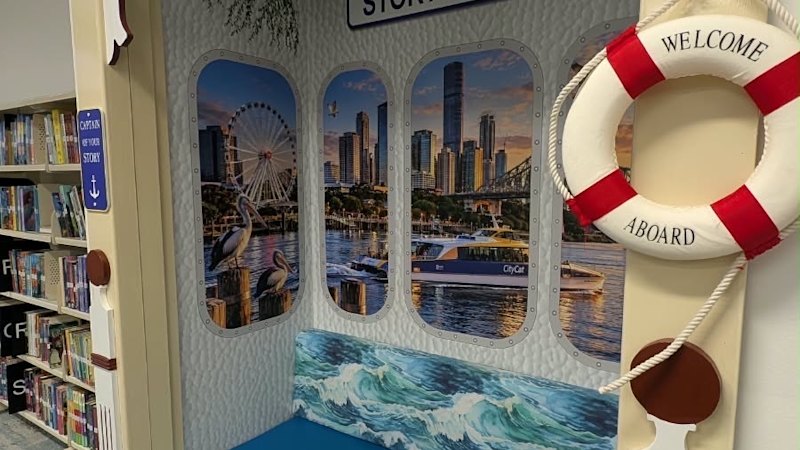 Call to regulate AI use in public art after Brisbane mural backlash
 Police probe after teacher allegedly sold drugs and alcohol to students
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability