[CRITICAL] 2026-021: High Severity Vulnerability in Java SE and OpenJDK
ThreatFilter threatfilter.dev
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) On 17 November 2026, Oracle and the OpenJDK project released fixes for CVE-2026-114938, a high severity vulnerability in OpenJDK which could lead, under certain circumstances, in unauthenticated Remote Code Execution (RCE).<br> CERT-EU recommends updating vulnerable version of OpenJDK, prioritising internet facing applications.<br>
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
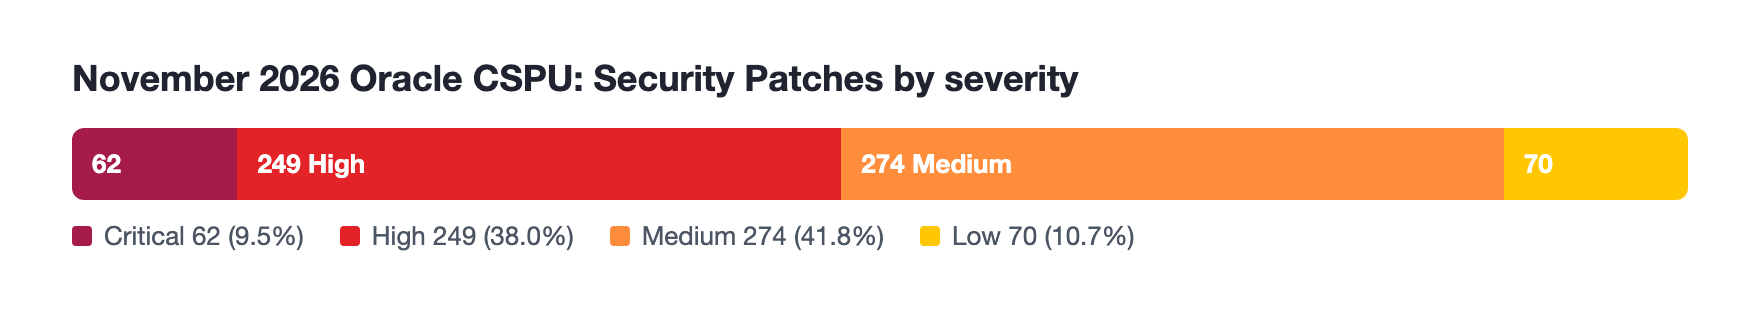 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
 U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks
 Whole-of-state defense: How SLED agencies can secure critical infrastructure in the AI era
 Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)