CVE-2026-99313 — In the Linux kernel, the following vulnerability has been resolved: HID: logitech-hidpp: fix race condition when accessing stale stack poin
ThreatFilter threatfilter.dev
Listen to this summary
(vendor/severity tags below are heuristic) In the Linux kernel, the following vulnerability has been resolved: HID: logitech-hidpp: fix race condition when accessing stale stack pointer The driver uses hidpp->send_receive_buf to point to a stack-allocated buffer in the synchronous command path (__do_hidpp_send_message_sync). However, this pointer is not cleared when the function returns. If an event is processed (e.g. by a different thread) while the send_mutex is held by a new command, but before that command has updated send_receive_buf, the handler (hidpp_raw_hidpp_event) will observe that the mutex is locked and dereference the sta
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
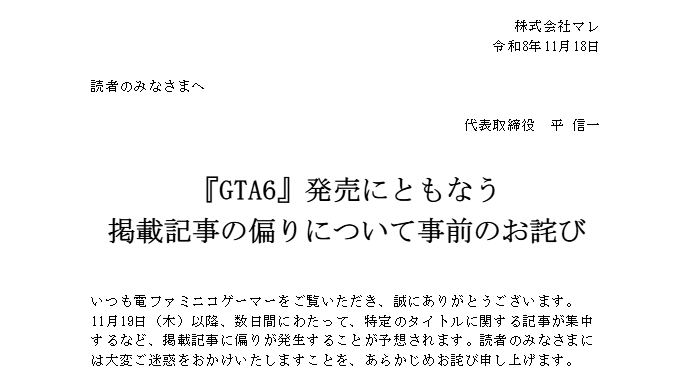 Denfaminicogamer releases an advance apology for the imbalance in article coverage following GTA 6's release
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
 Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)