CVE-2026-99312 — In the Linux kernel, the following vulnerability has been resolved: KVM: x86: Unconditionally reset MMU context when emulating INIT Force
ThreatFilter threatfilter.dev
Listen to this summary
(vendor/severity tags below are heuristic) In the Linux kernel, the following vulnerability has been resolved: KVM: x86: Unconditionally reset MMU context when emulating INIT Force an MMU reset when emulating an INIT even if paging was already disabled, as the MMU page role includes guest_mode (L2), i.e. an INIT while L2 is running with CR0.PG=0 will result in KVM running L1 with a stale MMU context. Alternatively, the reset could be scoped strictly to paging being enabled or L2 being active, but SMM is also encoded in the page role. Even though it _should_ be impossible for the vCPU to be INIT'd while SMM is active, there's zero value
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
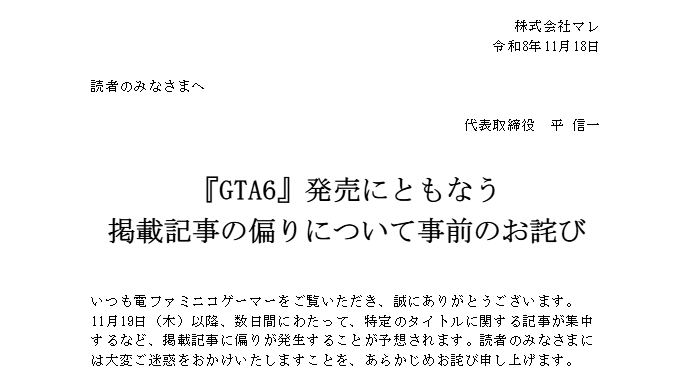 Denfaminicogamer releases an advance apology for the imbalance in article coverage following GTA 6's release
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
 Brotli2Shell: Frequently asked questions for Google Brotli decoder vulnerability (CVE-2026-111497)