[CRITICAL] Java4Shell (CVE-2026-114938) Enables Pre-Auth RCE in Jira, Jenkins, Keycloak on Java 17+ AVX-512 VBMI Servers
ThreatFilter threatfilter.dev
This is what was read here when it was published. threatfilter.dev no longer carries it in what it publishes now.
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) A Java flaw called Java4Shell can let attackers without an account run their own code on Jira, Jenkins, Keycloak, and three other widely used applications, says Calif, the security research firm that disclosed it this week. The flaw is present in Java 17.0.6 and later, and the vulnerable code runs only on x86-64 Intel and AMD chips that support the AVX-512 VBMI feature. Tracked as
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
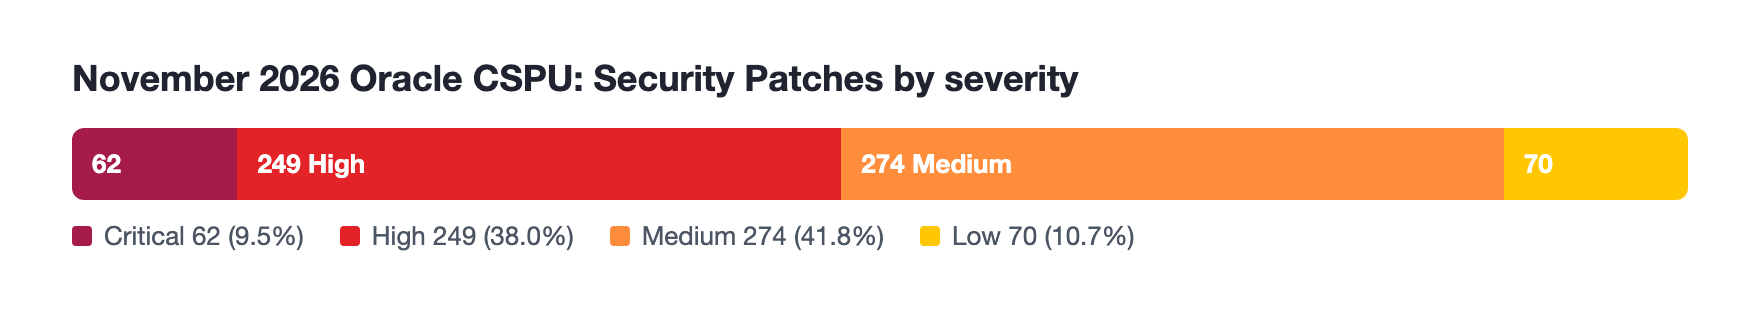 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)
 U.S. urges critical infrastructure orgs to secure refrigeration systems ASAP after EU supermarket and blood bank attacks
 Whole-of-state defense: How SLED agencies can secure critical infrastructure in the AI era